What is SIEM? It is one of the first questions IT teams face as the number of servers, firewalls and endpoints grows. SIEM (Security Information and Event Management) is a security platform that collects log data from different systems in one place, correlates those records and turns suspicious behavior into alerts. Although the name is sometimes confused with brands like Siemens, SIEM is not a product name; it is a security discipline.
This guide explains, in plain terms, the difference between a SIEM system and basic log management, how it works step by step, how it relates to a SOC and the mistakes most often made during deployment. What businesses expect is clear: detect attacks faster, get to the evidence quickly during an incident and present orderly records during audits. At the end of the article, in-house and managed SIEM options are also compared.
Your Logs Are Collected, but Is Anyone Reading Them?
The MAV Cloud team reviews your current log sources, retention period and alerting setup together with you. By the end of the first call, it is clear where to start.
What is SIEM and what problem does it solve?
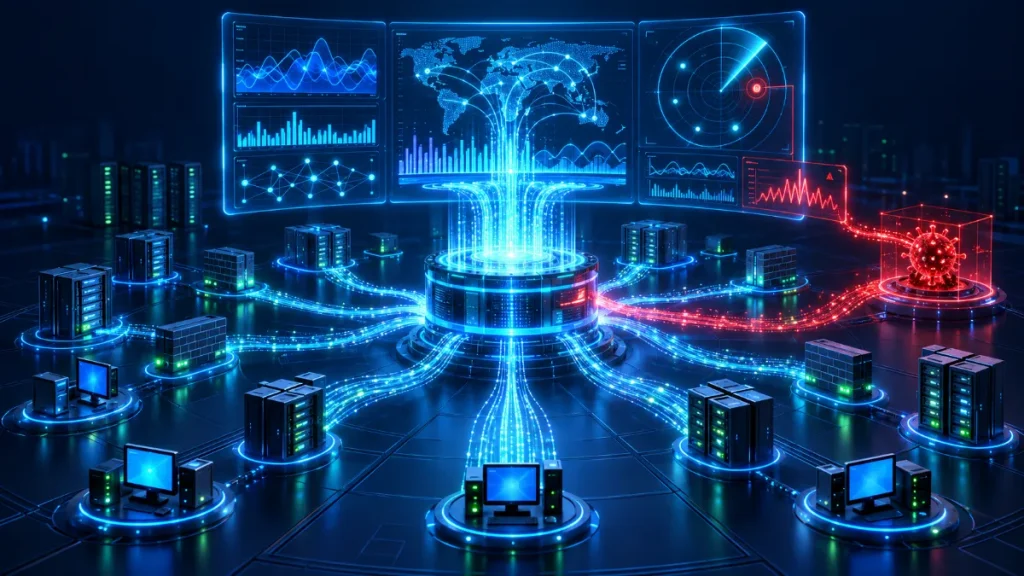
In short, SIEM is a centralized monitoring layer that collects security-related event records and makes sense of them. Every day in a typical organization, firewalls, VPNs, Active Directory, mail servers, databases and endpoint agents generate millions of lines of logs. As long as those records sit in separate systems, piecing together the parts of a single attack is nearly impossible.
A SIEM solution removes that fragmentation. Take a VPN login from abroad on a user account at midnight, followed by that same account being added to the administrators group, and shortly afterwards bulk encryption starting on the file server. Viewed individually, these are three ordinary-looking events. When a correlation rule sees all three together, it raises a high-priority alert.
Product marketing usually describes SIEM through a feature list. The core capabilities of these platforms are:
- Log collection: Centralized intake of records from servers, network devices, cloud services and applications.
- Normalization: Converting records in different formats into common fields (user, IP, time, event type).
- Correlation rules: Linking events from different sources by time and context.
- Alerting and reporting: Prioritized alerts, dashboards and audit reports.
- UEBA: User and entity behavior analytics to detect unusual behavior.
- Long-term retention: Archiving records with their integrity preserved for post-incident investigation and regulatory requirements.
How does a SIEM system work? The process in 5 steps
The technical answer to “what is SIEM” lies in the path the data takes. The process starts at the source and ends with incident response; if any link in the chain is weak, the platform loses value. The sequence below is the generally accepted flow in enterprise deployments:
- Collection: Logs are brought to the central platform via agents, syslog, API connections or cloud integrations. Which sources to collect is decided based on a risk analysis.
- Normalization and enrichment: Records are mapped to a common schema; location is added to IP addresses, department to users and criticality to assets.
- Correlation: Rules and behavioral models turn individual events into meaningful scenarios. A brute-force attempt followed by a successful login is the classic example.
- Alerting: The matching scenario lands on the analyst’s screen with its severity and context. In a well-designed alert, “what happened, on which asset, by which user” can be answered at a glance.
- Incident response: The analyst validates the alert, contains the impact (locking the account, isolating the endpoint), investigates the root cause and documents the process.
One of the core references for log management practice is NIST’s SP 800-92 Guide to Computer Security Log Management. It gives organizations a framework for planning log sources, setting a retention policy and defining analysis responsibilities.
SIEM vs. log management vs. SOC: what’s the difference?
These three terms are often used interchangeably, but their scope is different. Log management collects and stores records; SIEM analyzes those records and generates alerts; a SOC is the team and process that monitors, interprets and responds to those alerts 24/7. Put simply, the difference between SIEM and SOC is the difference between a tool and the operation that uses it.
| Criterion | Log management | SIEM | SOC |
|---|---|---|---|
| Core function | Collection, storage, search | Correlation, alerting, reporting | Monitoring, analysis, incident response |
| Output | Archived records | Prioritized alerts | Validated incidents and actions |
| Staffing need | Low | Moderate, for rule management | 24/7 analyst team |
| Threat detection | Limited to after-the-fact search | Near real time | Real time and contextual |
Once it is clear what SIEM is and where the SOC begins, the architecture becomes clear too. In practice, a mature security architecture uses all three together. EDR/XDR agents on endpoints produce deep telemetry, SIEM combines that telemetry with network and identity logs, and the SOC team validates the resulting alerts. How endpoint visibility is achieved is covered on our EDR/XDR endpoint security page.
Common practice vs. the right approach: in-house or managed SIEM?
In many organizations, common practice is to buy a SIEM license, install it and leave the rules at their defaults. A few months later the console is full of hundreds of alerts nobody reviews. The right approach is to treat the platform not as a product but as a service that needs continuous tuning.
During procurement, the question of what SIEM is shifts from a technical definition to a question of operating model. The decision points for the options can be summarized as follows:
- In-house deployment: Gives full control, but hardware or cloud capacity, licensing, rule development and 24/7 analyst coverage are all the organization’s own responsibility.
- Managed SIEM: Deployment, source integration, rule tuning and monitoring are handled by the service provider, freeing the internal team for decision-making and improvement work.
- Hybrid model: The platform stays in-house while monitoring and rule maintenance are shared with an external team. It is a common choice for mid-sized organizations.
The real question behind the choice is who will read the alerts at night and on weekends. Without an answer to that, even the most advanced platform remains just an expensive archive.
In-House or Managed SIEM? A Pre-Decision Assessment
We can prepare a short preliminary assessment that compares both models side by side based on your number of log sources, retention needs and internal team capacity.
Which logs should you collect? Prioritizing sources
Collecting every log drives up both cost and noise; collecting none leaves blind spots. Sources should be chosen with the attacker’s likely path in mind. The Best Practices for Event Logging and Threat Detection guide, co-published by the US cybersecurity agency CISA, also recommends prioritizing sources based on organizational risk.
How you answer the question of what SIEM is shapes source planning: if the platform is seen as an archive, everything gets collected; if it is seen as a detection tool, the use cases are written first. The first phase usually starts with these sources:
- Identity systems: Active Directory, Entra ID, VPN and multi-factor authentication logs
- Network security: firewall, IPS, web proxy and DNS logs
- Endpoints: EDR/XDR telemetry and server operating system event logs
- Critical applications: ERP, database access logs, email security gateway
- Cloud and virtualization: management console access and privilege changes
Business applications and lower-risk sources are added in the second phase. As sources are added, correlation rules need to be reviewed as well; otherwise the new data only adds storage cost.
KVKK, Law No. 5651 and log retention: what to watch for in Türkiye
For businesses operating in Türkiye, log management is not just a technical choice. KVKK (Türkiye’s Personal Data Protection Law, Law No. 6698) requires data controllers to take appropriate technical and administrative measures to keep personal data secure, and keeping and monitoring access logs is a natural part of those measures. Current guidance and Board decisions are available on the Personal Data Protection Authority website (in Turkish).
Under Law No. 5651, certain types of providers also have obligations to retain traffic data; the period and scope vary by provider type. Storing logs on infrastructure hosted in Türkiye, with their integrity preserved and closed to unauthorized access, makes audits considerably easier. The information in this section is general in nature and is not legal advice; work with legal counsel on how these obligations apply to your organization.
From a regulatory standpoint, SIEM is a control mechanism that keeps the integrity of records and access trails in a provable way. For organizations that want to address the technical and administrative sides of compliance together, KVKK security consulting is a good starting point.
Common mistakes in SIEM projects and the right way to handle them
Projects that answer “what is SIEM” with “software that collects logs” tend to fall into the same traps. Most problems come not from technology but from gaps in scope and process.
- Collecting every log but analyzing none: Terabytes of records pile up, but no rules are written. The right approach is to define use cases first (e.g., account takeover, privilege escalation) and select logs accordingly.
- Alert fatigue: Default rules generate hundreds of false positives, and analysts miss the critical alert. Rules should be tuned to the organization’s traffic in the first weeks and reviewed regularly.
- Skipping time synchronization: On sources with inconsistent NTP settings, events appear in the wrong order and correlation breaks down.
- Generating alerts without a response plan: When an alert fires, who takes which step and within what time should be written down.
- Leaving the retention policy undefined: If hot (quickly searchable) and cold (archive) retention periods are not planned from the start, costs spiral out of control.
What successful projects have in common is that the SIEM platform is treated as a living system. When a new application goes live, its log source, rules and response steps are updated in the same change record.
What to look for in a reliable SIEM service
Once your organization has answered what SIEM is, the next question is the service model. When choosing a managed security event management service, evaluate the process and standards behind it rather than the product name. Because log data contains an organization’s most sensitive information, the provider’s information security management system should also be audited.
MAV Cloud operates with ISO/IEC 27001 information security, ISO/IEC 27701 privacy information management, ISO 22301 business continuity, ISO 9001 quality and ISO/IEC 20000 service management certifications. Its infrastructure is located in an Equinix data center in Türkiye, with 24/7 system monitoring and expert support. Under the SLA, the defined first-response target for critical situations where the service is completely unavailable is 15 minutes.
It is also worth asking a provider what SIEM means to them during selection; the answer shows whether they are selling a platform or an operation.
When evaluating a service proposal, these questions help: Which log sources are in scope, how often are rules updated, how many minutes does it take for an alert to reach an analyst and which metrics do the monthly reports include? A service model with written answers to these questions keeps surprises to a minimum. MAV Cloud’s approach is described in detail on the SIEM and log management service page, and the 24/7 monitoring and response side on the SOC service page.
Frequently Asked Questions
What is SIEM and what does it do?
SIEM (Security Information and Event Management) centrally collects security logs from different systems, correlates them and turns suspicious activity into prioritized alerts. The goal is to detect attacks early and reach the evidence quickly after an incident.
What is the difference between SIEM and log management?
Log management collects and stores records and makes them searchable. SIEM runs correlation rules on those records to provide near real-time threat detection and alerting.
What is the difference between SIEM and SOC?
SIEM is a technology platform; a SOC is the team and process that monitors, validates and responds to the alerts coming from that platform 24/7. The two work together for effective security monitoring.
Do small and mid-sized businesses need SIEM?
Risk profile matters more than headcount. For businesses that process personal data, use remote access or have multiple locations, a managed SIEM solution is a more accessible path than building an in-house team.
How long does a SIEM deployment take?
It depends on the number of log sources, the integration method and rule tuning. A phased plan starting with critical sources is typical, and rules are fine-tuned to the organization’s traffic during the first weeks.
How long should logs be retained?
The retention period is set based on internal policy, industry regulations, measures under KVKK and obligations arising from legislation such as Law No. 5651. Get advice from legal counsel on the period that applies to your organization.
What is UEBA and how does it relate to SIEM?
UEBA (User and Entity Behavior Analytics) is an analytics approach that learns the normal behavior of users and devices and detects deviations. Many SIEM platforms include UEBA capabilities to complement rule-based correlation.
How can you prevent alert fatigue?
Tuning default rules to the organization’s traffic, consolidating low-value alerts and defining written response steps for each alert type significantly reduce alert fatigue.
Make Security Monitoring Visible 24/7
A free preliminary assessment of your current log infrastructure shows which sources are missing and which alerts are unnecessary.
For IT managers just starting to research what SIEM is, the first step is to list your current log sources. Organizations torn between an in-house deployment and a managed service can start with one question: who will read the alerts at night? Teams ready to act can quickly get a snapshot of where they stand by requesting a free assessment.